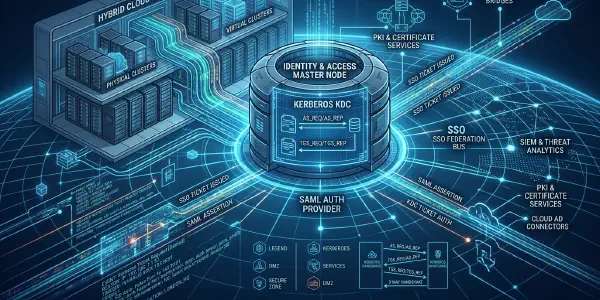
Kerberos Cross-Realm Trust
Kerberos cross-realm authentication relies entirely on TGS exchanges between KDCs. Understanding the three-step ticket flow makes it easier to troubleshoot trust relationships between domains.
read more
Kerberos Debug Mode for the JVM, Spark, and SPNEGO
Enable Kerberos debug logging in a JVM, Spark driver, and Spark executors to troubleshoot SPNEGO and authentication issues. Covers the exact Java system properties, Spark configuration keys, and how to redirect Spark logs to stdout so Kerberos output interleaves with application logs.
read more
Kerberos Shortname Mapping (Auth_to_Local)
A practical walkthrough of how Hadoop maps Kerberos principals to short names via the auth_to_local property, including rule syntax, acceptance filters, and common troubleshooting patterns.
read more
Multiple HTTP Service Principal Names
How to verify and manage HTTP service principal names in Active Directory using ldapsearch and setspn, including a note about Centrify’s uppercase requirement.
read more
Name Node Trash Check Point Interval & TGTs on Non-HA NN with KMS
Adjusting the NameNode trash checkpoint interval can resolve TGT renewal issues on non-HA NameNodes using KMS. This change is safe and does not affect trash retention.
read more
Wrong Number! Taming the Kerberos Identity Crisis
A practical look at why the MIT krb5 KDC rejects a TGS-REQ with KRB_AP_ERR_NOT_US, including the exact validation logic and the most common root causes behind the error.
read more